Codex Data Analysis: Scope, Then Audit
By William Zhu (independent public engineering profile: GitHub @allwefantasy; no personal LinkedIn) & the InfiniSynapse Data Team · Published: 2026-08-22 · Last updated: 2026-08-28 · Last verified: 2026-08-28 · Next review: 2026-11-28 · About · Editorial standards · Privacy · Publishing terms · Corrections
Table of Contents
- TL;DR
- What codex data analysis actually is
- A same-CLI framework
- How Codex differs from a first-editor habit
- Tool landscape when Codex arrives
- Implementation steps for a scoped Codex task
- Desk sample: second client, same folder (InfiniSynapse desk log)
- How to cite this page
- Selection scorecard
- Failure modes that leak or stall
- Frequently Asked Questions
- Conclusion
TL;DR
We evaluate second-client reuse at the InfiniSynapse desk on sanitized composites; first-party figures on this page are desk log CDX-SAME-FOLDER-20260822, not customer uplifts and not a third-party bake-off.
Direct answer: codex data analysis uses OpenAI Codex as a configured client. The optional agent_infini interface, client instructions, and /tasks workspace are separate InfiniSynapse components, not native Codex features. Use independently scoped credentials per person, device, and environment.
Download evidence: desk log · aggregate CSV · verify script. These files record this desk run as a first-party sanitized composite.
What you'll learn:
- Why the workflow fails when it grows a private credential path
- How Codex reuses
task new,db ls, andrag enable - Why each person, device, and environment needs revocable credentials
- Desk log
CDX-SAME-FOLDER-20260822, of a second client writing into the same folder - Failure modes that make the second client look independent while it is just another caller
OpenAI’s Codex documentation defines the official product surface, and the official Codex repository documents the CLI. OpenAI’s Codex security guidance explains sandboxing and approvals. These sources support client capability claims; they do not document or endorse InfiniSynapse. Retrieved 2026-08-28.
What codex data analysis actually is
Key Definition: In this article, codex data analysis is a first-party operational pattern: configure Codex permissions, provide a scoped credential to an authorized interface, start a goal, and let a reviewer inspect persistent task artifacts.
Codex configuration supports precise claims about client settings. Codex MCP documentation describes external tool connections. Neither makes agent_infini, its instructions, or /tasks native integrations.
Author qualifications and accountability
William Zhu is an InfiniSynapse cofounder. His public GitHub profile and repositories auto-coder, byzer-llm, and BYZER-RETRIEVAL verify identity and engineering work. They do not independently validate this method, product, or desk log. No degree, customer, media review, certification, OpenAI recognition, or independent assessment is claimed. 2026 WAIC Future Tech OPC Excellence Award (homepage; not a review). 2026-07-29 attestation.
Internal terms this page uses: a client is separately configured. The shared folder is a first-party /tasks workspace. A credential policy defines minimum scope and revocation; it never means one shared secret.
Whether db ls returns an authorized source depends on the separately configured first-party CLI and credential scope, not Codex model capability.
codex data analysis is not “paste a CSV into Codex and ask for a plot.” That is file babysitting. Used well, Codex states a standing goal, the data agent plans, and the artifacts show up in /tasks.
Spider 2.0 and the BIRD benchmark paper illustrate enterprise text-to-SQL complexity. They do not test this workflow or validate its artifact counts.
For codex data analysis, those benchmarks motivate careful SQL review rather than a product-performance claim.
Chat with your data is the same goal without Codex. Keep both paths pointed at one task object.
The codex data analysis method records the client as metadata while keeping task evidence independently accessible.
Codex is a second client
Configure Codex instructions independently. Use a separately scoped credential that can be revoked without affecting another person, device, environment, or client.
Not a reason to fork sources
If the policy permits a read-only replica, Codex may receive equivalent source authorization through its own credential. A write-capable URI added for convenience is a process failure.
A same-CLI framework
| Piece | Owner | What “good” looks like |
|---|---|---|
| First editor | Existing habit | Cursor or Claude Code already starts tasks |
| Codex | New client | Separate instructions and scoped credential |
| CLI | Shared | agent_infini is not reinstalled as a fork |
| Sources | Product | db ls matches across clients |
| Artifacts | Task workspace | One folder shape, whoever started the job |
codex data analysis is the new-client row. Everything else should look boring.
Issue credentials according to one policy: minimum scope, named owner, no frontend exposure, and independent revocation.
Every codex data analysis credential should have a documented owner, environment, scope, and revoke path.
Configure instructions, never copy secrets
Client-specific instructions may teach Codex how to call an authorized first-party interface. Never place credentials or source connection strings in those instructions.
Same folder, same review
Reviewers should not have to ask “was this a Codex run?” The task folder answers with steps, SQL, and files. Exploratory data analysis still happens inside that folder. The client name is metadata, not a second archive.
Review codex data analysis artifacts against source permissions and the recorded goal, not client branding.
How Codex differs from a first-editor habit
The first editor trained the team to open /tasks. codex data analysis must not untrain them. Codex users often expect a local session log. That log is not the record. Open the same folder.
If artifacts differ for the same goal and authorized source, compare configuration, permissions, prompts, versions, and execution evidence before attributing the difference to a model.
Data visualization in the workspace is the chart you can download. A Codex-only screenshot is not a chart the team can cite.
A codex data analysis chart is evidence only when its source, query, and artifact remain inspectable.
Tool landscape when Codex arrives
Cursor / Claude Code. Separate clients with their own configuration and credentials.
Codex. Configure sandbox, approvals, first-party instructions, and a scoped credential.
Gemini CLI. Another separately configured client under the same policy.
Web Chat. Still the teaching surface for people who will never install Codex.
This comparison keeps codex data analysis client-specific while applying one organization-wide authorization policy.
InfiniSynapse does not ask you to migrate so Codex can work. Connect the existing database or files, bind a knowledge base if you have one, then let Codex start the task. Private deployment and desktop exist; the check still starts on the web console.
For codex data analysis, source access comes from explicit authorization rather than the model’s inferred capability.
Zero-config against a replica you already run is enough. The product is a professional data analyst, not a ChatBI box that only emits SELECT. Multimodal inputs and 100+ file formats still land as task artifacts when you attach files the product already accepts. Codex does not become a new ingestion bus, and it does not write definitions back into production.
If the first editor already bound a knowledge pack to the orders replica, Codex should retrieve the same pack. If it does not, the bind is wrong—not “the new model needs its own notes.” Organization memory is the bound pack plus the task folder. A Codex session log is not memory. AI-native boards, if a goal produces one, are files in that folder, not a tile catalog you must pre-build for Codex.
Do not build a Codex warehouse
There is no such object. There is a source list and a task list. codex data analysis that demands a shadow schema is a buying conversation you should leave.
Well-scoped codex data analysis reuses governance policy without reusing another user’s credential.
Implementation steps for a scoped Codex task
- Configure Codex permissions. Record Codex version, config, sandbox, and approval policy. Expected result: Tool boundaries are explicit.
- Issue a scoped credential. Assign it to one person, device, and environment without publishing the value. Expected result: It can be revoked independently.
- Configure the first-party interface. Record CLI and instruction hash and authorized source permissions. Expected result: Source visibility matches granted scope.
- Start a standing goal. Record goal, run ID, timestamps, and status. Expected result: One identifiable task begins.
- Review SQL and artifacts. Record SQL, memo, chart, and verification hashes. Expected result: The evidence is inspectable.
- Have a reviewer reopen it. Preserve all failures and wall clock. Expected result: A reviewer without Codex can open the same task.
Before installation, define the credential and source policy; never plan to reuse another user’s secret.
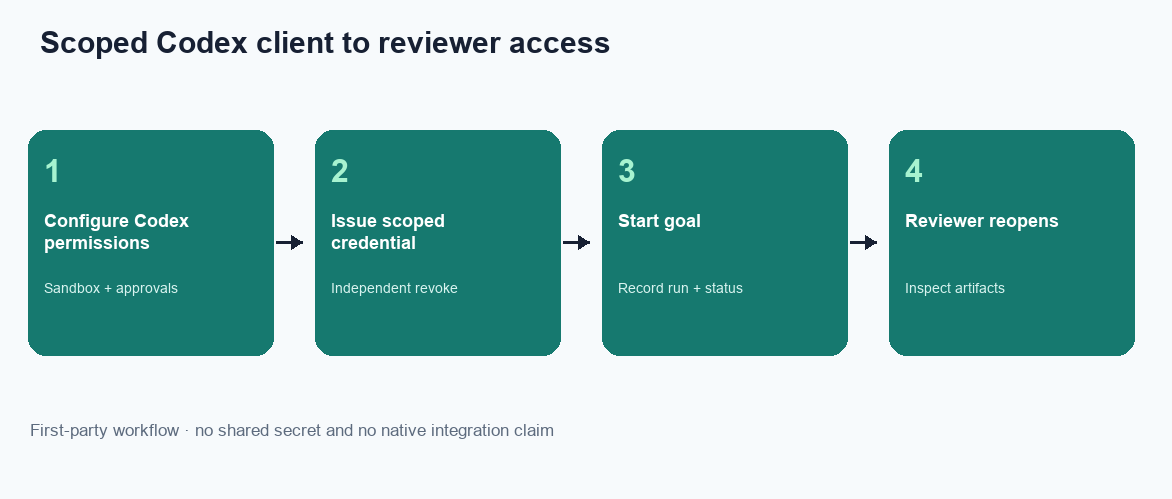
Figure. Educational four-step sequence the desk uses to tell a Codex session log from a shared folder. Expected result after step 6: a Cursor user opens /tasks and finds the same plan, SQL, memo, and chart the Codex session claimed were done. Not a product screenshot or a customer SLA.
Write the standing goals on one page: weekly ops pack, experiment readout, finance exception list. codex data analysis should start those goals with the same nouns Cursor uses. If Codex invents a new name for “active store,” the bind failed. Fix the pack. Do not add a Codex glossary. Pin agent_infini on the image so a second install path “for Codex nightlies” cannot start a different task.
Configure client instructions
Codex does not inherit instructions from Claude Code, Cursor, or Gemini. Review first-party instructions separately and keep secrets out of prompts and session logs.
Open the same folder
The first successful codex data analysis run—and the only one that counts—is the one a Cursor user can audit without Codex. Click the task. Read the plan. Open the SQL. Download the file. If those three things fail, Codex did not finish even if the session said “done.”
Desk sample: second client, same folder (InfiniSynapse desk log)
This is a first-party InfiniSynapse desk log of codex data analysis writing into the same folder, not a named-logo customer case and not an uplift claim. Run ID: CDX-SAME-FOLDER-20260822. Date: 2026-08-22 (Tuesday). Operator: InfiniSynapse Data Team. Source: a read-only replica the desk is authorized to read. Goal asked twice: “same experiment readout as last week.” Download the same numbers as desk log CDX-SAME-FOLDER-20260822.
Tuesday, an engineer who prefers Codex started that goal. codex data analysis created a task.
| Retrieval state | Task id | Memo | Chart | A/B note check |
|---|---|---|---|---|
| Codex local only | 1 | 0 | 0 | 0 |
| First-party shared task | 1 | 1 | 1 | 1 |
About eighteen minutes later (wall-clock; warehouse time excluded) the shared folder held a Markdown memo, one chart, and a slice that a reviewer could check against the A/B definition in the bound notes. Cite this table only as first-party desk log CDX-SAME-FOLDER-20260822; the honest claim is limited to its artifact counts and wall clock.
The next week, Cursor started the same goal. The folder shape did not change. That is the point: the client rotated, the trail did not.
In codex data analysis, persistent artifacts matter more than a confident local completion message.
The reviewer checked three objects: the retrieved passage for the experiment grain, the SQL against the replica, and the chart file. None of those objects named Codex. The extract was a CSV, not a write-back.
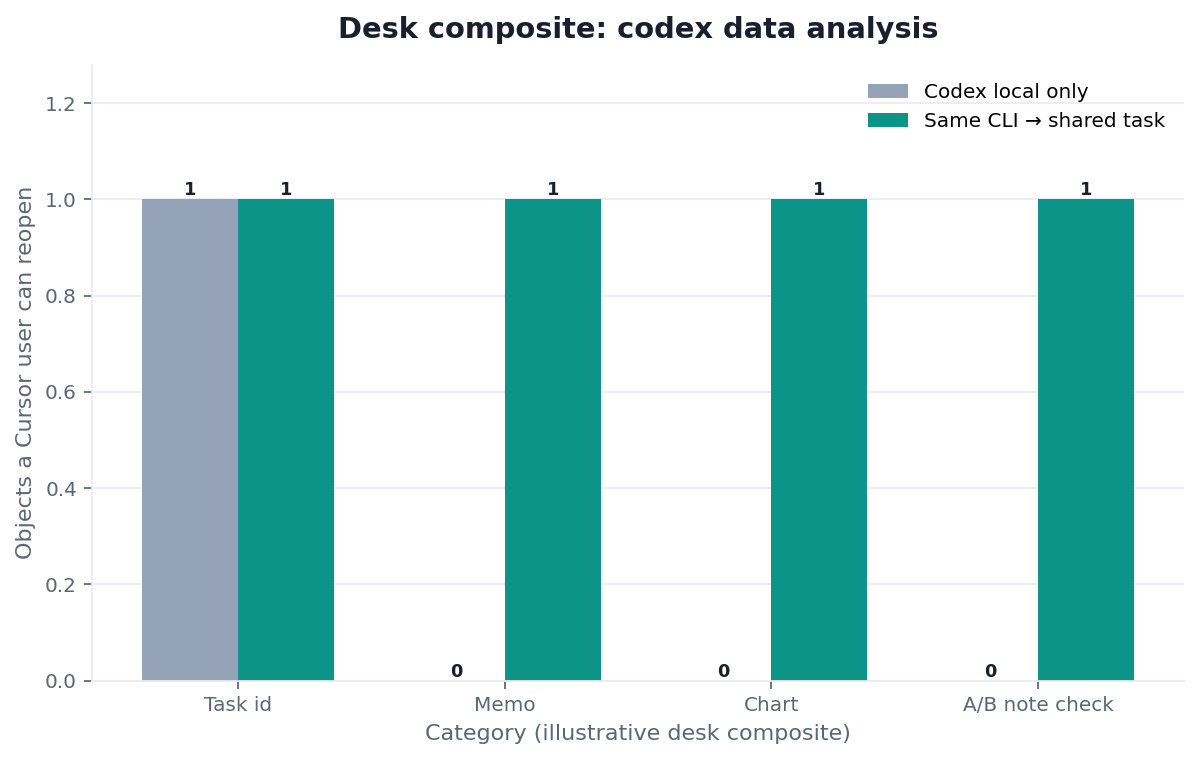
Figure. InfiniSynapse desk log CDX-SAME-FOLDER-20260822: Tuesday Codex start; Cursor reviewer opened /tasks. Local-only left 1 / 0 / 0 / 0; shared CLI left 1 / 1 / 1 / 1. Published context: the independent sources linked in the body. Not a customer experiment, SLA, or official benchmark.
Evidence boundaries and external validation status
Desk log CDX-SAME-FOLDER-20260822, its Markdown file, and aggregate CSV are first-party sanitized demo evidence. They are not a customer case, independent benchmark, third-party dataset, OpenAI test, certification, media evaluation, or endorsement. No independent party had reproduced the run as of 2026-08-28.
Accordingly, codex data analysis results here remain first-party observations awaiting independent replication.
Replication should disclose Codex version, config, sandbox, and approval policy; CLI and instruction hash; credential scope without the value; source permissions; goal/run ID; timestamps/status; SQL and artifact hashes; local-only baseline; all failures; wall clock; and conflicts of interest.
| Evidence class | What you can cite | What you cannot claim |
|---|---|---|
| Desk log on this page | Same folder across clients, artifact counts 1/0/0/0 → 1/1/1/1, ~18 min wall-clock, run ID, downloadable log | Customer uplift %, vendor bake-off win, named-logo case |
| Markdown and aggregate CSV | Two observations, method, counts, reviewer flag | Raw, source, customer, or third-party data |
| OpenAI documentation | Codex client, sandbox, approval, configuration, and MCP behavior | Native agent_infini or /tasks support |
| Research and standards | SQL complexity, provenance, tracing, secure development, and risks | Independent validation of this workflow |
How to cite this page
Page: Zhu, W., & InfiniSynapse Data Team. (2026). Codex Data Analysis: scope, then audit. InfiniSynapse
Run: InfiniSynapse Data Team. (2026). Desk log CDX-SAME-FOLDER-20260822 (sanitized composite)
Neither is an audit. Cite the artifact counts. No independent reproduction exists. Send contradictions to zhuhl@infinisynapse.com.
Selection scorecard
| Criterion | Weak second-client use | Strong second-client use |
|---|---|---|
| Identity | Shared team secret | Scoped credential with independent revoke |
| Instructions | Copied from another client | Codex-specific reviewed configuration |
| Evidence | Session log | Shared task folder |
| Sources | Extra URI for the new model | One authorized list |
| Review | “Ask the Codex user” | Anyone opens /tasks |
If a pitch for codex data analysis cannot show the same folder Cursor already uses, score it as a fork. If it can show the folder but wants the key in application code, stop. A local session that prints SQL is still a copilot. A task folder that a Cursor user can download is the analyst object.
The practical codex data analysis acceptance test is reviewer access to the recorded evidence.
Review client instructions as code: pin their version, hash changes, and test only within the authorized source policy.
Failure modes that leak or stall
A shared credential path
Someone pasted a team credential into a wiki. Revoke it. codex data analysis should use a separately scoped credential under the same policy.
Codex as the warehouse
People ask Codex to “just write the table.” InfiniSynapse does not write production definitions. codex data analysis that aims a write-capable URI at a live host is a process failure.
Unread folder after a confident session
Codex returned a paragraph. The task failed two steps later. Nobody opened the folder. Make “open /tasks” part of done for codex data analysis.
Teams should reject codex data analysis runs whose SQL, status, failures, or output files cannot be independently inspected.
Before production use, check that the credential is scoped and revocable, source visibility matches its permissions, a reviewer can open the task, and artifacts have hashes.
W3C PROV-O supports task and artifact provenance, while OpenTelemetry traces supports invocation chains. NIST SSDF SP 800-218 and the NIST AI RMF provide secure-development and AI-risk governance context. None tested this demo.
UK NCSC secure AI guidance, the OWASP GenAI/LLM Top 10, and GitHub secret scanning support lifecycle, threat, and secret-detection controls. They do not certify InfiniSynapse.
Related guides: Claude Code Features, Claude Code Install, What Is Claude Code, How Claude Code Works, Claude Coding, MCP for Data Analysis, Data Knowledge Base, Knowledge Base vs Semantic Layer, and Natural Language to SQL.
When the next missing object is not this page, open Gemini CLI Data Analysis when Gemini uses the same skill and the same task timeline, API Key for a Data Agent when Create the key in the task console; never ship it to a browser, or IDE vs Web Data Analysis when The IDE starts work; the web trail is what you share.
Run the Codex task, then open the same folder
Start the standing goal from Codex, then confirm the steps and files sit in the same workspace the first editor already uses. That is the same-CLI rule. This check uses only sources you authorize.
Commercial association: You do not need the workspace to complete the educational diagnosis on this page.
Open InfiniSynapseSourcing and accountability. William Zhu’s editorial profile and GitHub record verify identity and engineering work. OpenAI documents Codex; the other cited sources provide research and control frameworks. None validates InfiniSynapse. 2026 WAIC Future Tech OPC Excellence Award (homepage; not a review). COI: InfiniSynapse sells the first-party interface and workspace evaluated here.
Frequently Asked Questions
Does Codex need its own API key?
Bottom line: Use a separately scoped credential per person, device, and environment when feasible so it can be revoked independently.
Can Codex and Cursor share one Skill family?
Bottom line: They may follow the same policy, but each client requires its own reviewed instructions, permissions, and credential handling.
Where do the files go?
Bottom line: Into the shared task workspace. codex data analysis that only leaves a local session log does not have a team record.
What if I do not want to install Codex?
Bottom line: Use Cursor, Claude Code, the terminal CLI, or web Chat with the same sources and the same goal. Codex is a client, not a requirement. The educational diagnosis does not depend on the second client being installed.
Does OpenAI’s Codex documentation replace the same-folder rule?
Bottom line: No. OpenAI’s Codex docs describe the editor and CLI. They do not decide whether a Cursor user can open the same /tasks folder.
Is a Codex-only key the right way to isolate the new model?
Bottom line: Isolation should use scoped credentials, source permissions, sandbox controls, and independent revocation rather than a shared team secret.
Conclusion
codex data analysis is useful when client configuration, source authorization, credentials, and review evidence remain explicit. Start a goal only on authorized sources and treat the work as unfinished until another reviewer can inspect the recorded artifacts.